Case Study 01
Cybersecurity + Data Migration Support
teachingintothefuture.com • earthstudiosonline.com
I supported WordPress security, migration planning, subscriber cleanup, SEO, and troubleshooting across two client sites.
What I completed
- Reviewed what content could move safely and what needed to remain on WordPress.
- Prepared subscriber data, then held the bulk Substack import because it would email the audience automatically.
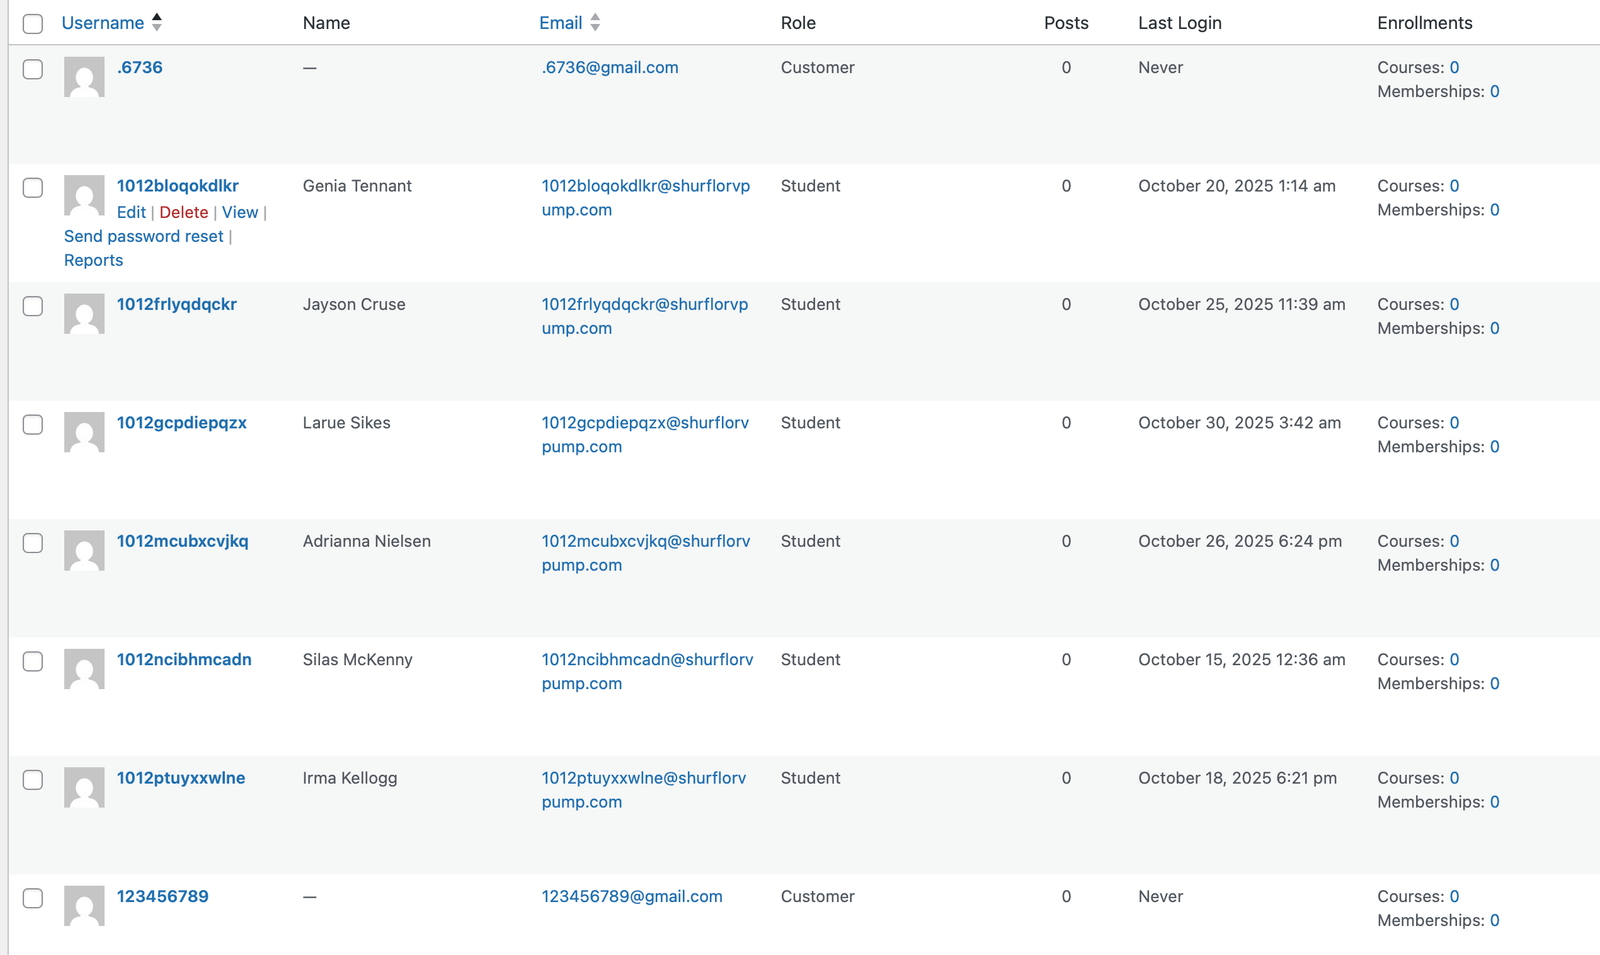
- Identified suspicious checkout and account patterns consistent with card-testing and bot activity.
- Cleaned suspicious Mailchimp subscribers and supported API key rotation after audience pollution concerns.
- Enabled reCAPTCHA and MFA and changed the default WordPress login path to limit automated login attempts.
- Completed front-end SEO work and cleaned the visible Substack integration and spacing on the live site.
- Updated the post-class follow-up email on earthstudiosonline.com so customers receive a delayed review and pottery pickup reminder.
- Escalated Redis and database instability to the hosting contact when the issue pointed beyond normal WordPress admin work.
Evidence
Proof snapshots
Selected proof images adapted from the internship.